Showing posts with label Security. Show all posts

How to encrypt your Facebook messages with Secret Conversations


Facebook's new encrypted messaging feature, Secret Conversations, is now live for everyone on Android and iOS.

 Good news, privacy enthusiasts: Facebook’s one-on-one encrypted messaging feature called Secret Conversations is now live for all Android and iOS users. 
Secret Conversations allows Messenger users to send end-to-end encrypted messages to their Facebook friends. There are a few caveats, however. First, it only works on a single device. Facebook says it doesn’t have the infrastructure in place to distribute encryption keys across your phone, tablet, and PCs.


You also have to explicitly start a Secret Conversation in Messenger. Encryption isn’t the default mode, and encrypted messages are not integrated into the primary thread of your conversations with a given contact.
In other words, if Alice and Bob have been chatting for years on Messenger, they’ll have to start a separate encrypted thread, and that encrypted thread will never integrate with their original, unencrypted thread.
That approach is very unlike what Facebook-owned WhatsApp is doing. The popular messaging platform automatically encrypts messages for all users if they have an encryption-compatible version of WhatsApp on their phone.
The final caveat for Facebook Messenger is that encrypted messaging only works in one-to-one messaging. Group conversations are not included in Secret Conversations.
Now that we’ve got the preamble out of the way, here’s how to use Secret Conversations. For our example, we’re using Messenger for Android but Messenger on iOS works similarly.

How to use Secret Conversations


 From the Messenger landing page, tap on your profile section, which is the person icon on the upper right of the screen. Scroll down until you see Secret Conversations and tap it. On the next screen, make sure the Secret Conversations slider is activated. Once it is, Secret Conversations are enabled for your device.
There are two ways to start an encrypted conversation in Messenger. The first is to create a new message as you usually do. Right at the top of the message creation screen you’ll see a lock icon next to a slider button. Click that and the screen theme changes color from blue to black. Now, choose the contact you want to start an encrypted conversation with, and you’re on your way.
After you send an encrypted message the person receiving it will have to agree to use the Secret Conversations feature. Once they do, they’ll see your message.
The second way is to initiate an encrypted conversation from a pre-existing message thread. Tap the i icon in the top right-hand corner of the message thread, and on the next screen tap Secret Conversation. The screen will turn to a black theme again, and you’re good to go.
To view an open secret conversation thread just choose it from the list of open message threads on the main screen of the app.
Secret Conversations work almost like regular Facebook messages but not quite. You can send text, emoji, stickers, and pictures; however, gifs, videos, voice calling, and payments are not supported.


Secret Conversations also offers a Snapchat-style self-destruct setting that you can adjust on a per-conversation basis. Open a secret conversation and then tap the stopwatch icon on the far right of the text entry area. This lets you set how long your messages remain visible on the other person’s device once they’re read. You can let them to last from 5 seconds to one day, or turn off the self-destruct setting altogether.
 That’s about all there is to the new Secret Conversations feature. You can use it as the standard way you talk to people on Messenger—though that’s a conscious choice you’ll have to make every time you start a new message thread—or just use it for sensitive topics.

Improve Your Online Privacy And Security Using NordVPN


Today, most users surf the web unaware of the fact that websites collect their data and track their locations – and if this is not enough, then there are hackers and cyber criminals who can easily steal sensitive data from the ill-equipped.

In short, the simple truth is that you have no or very little privacy when you're online.

So, if you're worried about identity thieves, or ISPs spying on or throttling your traffic, the most efficient way to secure your privacy on the Internet is to avoid using public networks; use a Virtual Private Network (VPN) instead.


When it comes to digital security, the first thing most users probably think of is a good Antivirus for protecting their sensitive data on their systems. But, what they forget is that the data they send over the Internet needs protection, too.

That's where Virtual Private Network (VPN) services come in.

VPN allows you to access a private network securely and to share data remotely through public networks, protecting your data online – much like a firewall protects your data on your computer.

The most important thing about a VPN is that it secures your internet connection to guarantee that all of the data you are sending as well as receiving is encrypted and secured from ISPs, hackers, and prying eyes.


It's because VPN works by overlaying a private network on top of a public network, effectively encrypting all the data that passes through the networks.

Since VPNs use a combination of dedicated connections and encryption protocols to generate virtual Peer-to-Peer (P2P) connections, even if snoopers did manage to steal some of the transmitted data, they would be unable to access it.

What's more, VPN makes sure that your real identity remains anonymous on the Internet so that no one can track the origin of your Internet connection back to you.

So, if you are worried about online safety and have not thought about getting a VPN, it might be time to use one. But, the real question here is:

Which VPN Service is the best that would take care of my security and anonymity seriously?


Many companies are providing VPN services, but not all are same. Some VPN services log all your browsing activities that nullify the point of using a VPN for privacy.
The best VPNs are the ones that do not keep logs or records of your browsing history and protect your anonymity, while offering a solid balance of features, server location, connectivity protocols, and price.
I came across some reputed VPN services, but they resolved few issues, and some addressed several issues but cost too expensive.

But, then I found NordVPN, the Panama-based company that has been providing advanced VPN services since 2012.

While reviewing, I found that NordVPN offers some good features, when it comes to privacy and security, though it might not be the fastest VPN service.

First and foremost, NordVPN is for those privacy-conscious users who prefer strong online anonymity at a very affordable price.

Below I have listed some key features of NordVPN.


1. No Logging

NordVPN is a real non-logging VPN, but that is just the starting point.

The company has a "strict no-logs policy when it comes to seeing user activity online."

On logging, NordVPN clearly explained that it makes its user's traffic "invisible to governments, ISPs, third party snoopers and even NordVPN.com" itself.


2. Headquartered Outside the US and EU

NordVPN is headquartered in the Central American country of Panama, but why does this matter?

NordVPN servers are operated under the jurisdiction of Panama – a country that doesn't require Internet service providers to monitor user traffic, so the company is "empowered to deny any third-party requests."


3. Double VPN System

A unique feature that NordVPN offers is its two-stage data encryption through its DoubleVPN service.

When using this service, user's data is passed through two separate VPN servers, which encrypt the data with AES-256-CBC cipher twice over using different keys as it leaves each server.

Re-encrypting the data twice will indeed make NordVPN more secure, which would make tracking an internet user more difficult.


4. Dedicated Tor-over-VPN Servers (for Maximum Anonymity)

Tor has become increasingly popular after Edward Snowden revelations about NSA's global surveillance programs.Tor is a great anonymity tool, but it also has certain downsides, like being a constant surveillance program target.

For those looking to get another layer of security protection, NordVPN is providing Tor-over- VPN server that encrypts your traffic before entering Tor network, making it even harder to trace back to the source.

Although Tor over VPN is only User → VPN → Tor → Internet, so your actual IP address is not masked from NordVPN. Much more useful would be a User → Tor → VPN → Internet kind of service that allows users to hide their true IP address from even the VPN provider.

Also, Tor is notoriously slow, which makes Tor-Over-VPN NordVPN servers slow in performance, but it would be unfair to judge something on factors beyond its control.

You can try the DoubleVPN with Tor-over-VPN for double-encrypted, multi-hop, maximum protection of your data. Isn't that cool?


5. Strong Encryption (2048-bit SSL for OpenVPN)

To protect your traffic from eavesdropping, NordVPN supports many different VPN security protocols, including OpenVPN, SSTP, PPTP, L2TP/IPsec and IKEv2/IPsec.

NordVPN for Windows, Linux or Mac OS allow users to manually choose between these encryption methods, while NordVPN custom apps for Windows, iOS, Mac OS and Android, have OpenVPN or IKEv2/IPsec protocols set by default, both open source, offering robust 2048 bit / 3072 bit encryption.


6. Automatic Kill-Switch

Besides its VPN services, NordVPN also offers a Kill Switch feature, which is a must-have for anyone who is genuinely concerned about security.

When configured, this feature constantly monitors the traffic between your selected applications or processes and the VPN servers.

If your VPN connection is interrupted or the data is broken at any point or for any reason, Kill Switch will automatically activate and immediately cut those apps or processes.

This is great, as it ensures that no unsecured data sneaks out.


7. Performance and Support (Hundreds Of Servers WorldWide)
Supported Platforms
Currently, the company has NordVPN apps for MAC OS, iOS, Windows, and Android.
NordVPN also supports Linux, but not Windows phone.

Users can even run NordVPN on game consoles and some network devices like routers.

In terms of speed, NordVPN provides consistent performance with several numbers of servers providing a satisfying rate.

NordVPN maintains servers and IP addresses in nearly 600 worldwide locations across 51 different countries, including:

The United States, United Kingdom, Canada, Australia, Brazil, Austria, France, Germany, Norway, Poland, Spain, Sweden, Switzerland, Romania, Russia, Iceland, Isle of Man, Israel, Italy, Hong Kong, Japan, Liechtenstein, Lithuania, Netherlands, New Zealand, Singapore, South Africa and more.

NordVPN offer servers that are customized for specific types of online access, such as high-speed servers for video streaming, Anti-DDoS servers for protection from denial of service attacks, and extra-secure servers for enhanced anonymity online.

Conclusion: NordVPN offers a solid suite of security and privacy features, with a wide choice of locations, clear logging policy, and good performance, in an easy-to-use package at a very reasonable price.
It's a smart choice and certainly should be on your shortlist. NordVPN provides different packages, from which you can choose one according to your requirement.

VPNs have now become a great tool not just for large companies, but also for individuals to improve their privacy and security online, dodge content restrictions and counter growing threat of cyber attacks.

So, if you are worried about your online safety, purchase a VPN now.

The best online backup service for securely encrypting your data


Many people resist backing up their data to an online backup service like MozyHome, Carbonite, or Backblaze because they worry their data will be poked through by company employees, hijacked by criminals, or provided to law enforcement or government agents without due process. 
The sanctity of your data boils down to whether the encryption key used to scramble your data can be recovered by anyone other than yourself. Below I outline the various methods and levels of encryption that can be employed by these services, and then evaluate six of the best options for home users. Several give subscribers full control of their encryption. If you’re already using a service, it’s possible you can even upgrade to take advantage of greater ownership options.


Choosing the services to evaluate

These are the parameters I set up for this roundup:

  • Focused on services that offer a personal edition, where you can purchase an account for a single computer or a bundle for a family 
  • Included services that are established or well-reviewed. 
  • Excluded services that offer scant information about their security and encryption practices. Subscribers should always be privy to how their data is protected. 
  • Excluded sync services, even those (like SugarSync) that offer continuous backup and versioning. I define a sync service as one that doesn’t encrypt data with a per-user key before being transmitted over a secure connection. That also leaves out Box, Dropbox, iCloud, Google Drive, and others.
  • I also bypassed services that offer bad advice about file retention or security practices, and ones whose information is years out of date.
Six companies remained after this winnowing: Backblaze, Carbonite, CrashPlan, iDrive, MozyHome, and SpiderOak ONE. Keep reading to see how they rate on encryption features and strength. 

Encryption: The ins and outs

Internet-hosted backups have several points of failure where encryption can protect a user’s data. I evaluated the services on each of these points:
Key possession. Encrypted backups require someone to create and possess the underlying key that’s used to encrypt your data before being stored by the host. But there are several aspects to this:
  • Who creates the encryption key? In all six cases, the native desktop backup software handles key creation, but with two services, you can opt to create a key.
  • Does the backup host hold the key in a form it can directly access, or in “escrow,” where it’s protected by a passphrase you set and the host doesn’t know? Or does the host never hold the key at all?
  • Is the passphrase converted through an algorithm into the actual encryption key, or is the passphrase used to unlock the encryption key? In the former case, an attacker who recovers the passphrase also effectively has the key, and can decrypt your backups.
If a backup service lets you reset your account password without losing access to your archives, it has full access to the encryption keys that guard your backups. If it can’t access your files’ contents (and sometimes even the listing of files) unless you enter your password or a custom key, you retain control.
Diversity of keys. Each service varies in whether it uses a single key for all backups, or various keys for different tasks. For instance, CrashPlan uses the same encryption key to scramble all backed-up files across all sessions; Backblaze generates a new key for each backup session; SpiderOak ONE has unique keys for every folder, version, and individual data block within its backups, partly to enable a group encrypted sharing option.
The more unique keys are used, the less risk you face from a single leaked or cracked key, or from advances in cryptographic cracking.
Encrypted before transit. Hosted backups require native apps to scan drives for files and transmit them. Strong encryption should be used by the app before files are transferred to a hosted service.
Encrypted in transit. It’s vitally important that transferred data is strongly protected separately from the encryption that wraps data before it’s sent. That’s to guard against offline attacks, where someone can intercept encrypted data and then attempt various ways to break it, both now and in the future. Encryption that’s unbreakable in 2016 may still break in the future. 
Protected at rest. Even encrypted data needs additional layers of security. Some hosts disclose additional information about how they safeguard your data, including certifications and audits from third parties.
Restoring files. When you restore a backup, there’s also a question of where the key winds up. Even for services that allow a user to create a custom full encryption key, that key has to be transmitted to the backup host in a form that can be decrypted in order to restore files. 
With all that in mind, we evaluated the following services from Excellent to Poor, summarizing their best and worst points in the pros and cons that follow each rating. For services that offer multiple ways to set up security and privacy, I’ve ranked based on the best method available, as outlined in the section above. 

Backblaze

Encryption rating: Very good
Pros:
  • Data is encrypted before and in transit
  • Website lets you access encrypted backups
  • Platforms: OS X, Windows, iOS, Android
Cons: 
  • Password is transmitted for recovery
  • Lacks a client that can restore and browse with local encryption keys
  • Unique keys can be unlocked with passphrase for master key
Backblaze uses public-key cryptography—the same kind of encryption used widely across the internet, including web connections with SSL/TLS cryptographic protocols. The app creates a public-private key pair and transmits the private key to its servers. For each backup session, Backblaze creates a new strong session key, and uses the private key in the key pair to encrypt it and send to its servers. The key is only stored in memory on the client and never stored in the clear at the server.


However, you can opt to set a passphrase to encrypt the private key before it’s transmitted to the server. In that way, this master private key and each session key are held in escrow. Only someone with the passphrase can access the private key, which in turn can decrypt a session key that restores data associated with a backup session.
Backblaze has engineered its system so that restores all happen via its website, not in the native computer app, so you have to enter that passphrase to decrypt the private key. The passphrase is also required for viewing information about backups through its website and mobile clients. The private key is also held only in memory on its servers and dumped when file browsing and restore operations finish.
This isn’t ideal. Backblaze falls short of other backup services by not offering a client that can handle restoring and browsing with encryption keys kept entirely locally. And while each backup session has a unique key, the fact that all can be unlocked with knowledge of the passphrase used to protect the master private key makes that less impressive. In practice, you’re more secure if you never restore files or browse lists.

Carbonite

Encryption rating: Excellent on Windows, Poor on Mac
Pros:
  • Data is encrypted before transit with Private Key encryption for Windows users
  • Website lets you access encrypted backups (only through Auto option)
  • Platforms: OS X (limited), Windows, iOS, Android
Cons: 
  • Data is encrypted before transit with Private Key encryption for Windows users, but not with Auto Encryption (Mac users' only choice)
  • Mac users get a server-side key that's stored on the server
Carbonite is a mixed bag. It offers only Windows users the opportunity to passphrase-protect a private key. Mac users rely on a server-side key that’s generated and stored there. Worse, Carbonite doesn’t encrypt Mac users' data before transmitting it with its default Automatic Encryption option; it encrypts only on the receiving end. That’s not the case with what it calls Private Key under Windows.


Because encryption happens on the far end, restored files are also decrypted before being transmitted back to a Mac user. Carbonite should step up and provide Private Key for Mac users, as the current situation doesn’t meet the bar for robust protection for backups or restores. 


CrashPlan

Encryption rating: Excellent 
Pros:
  • Data is encrypted before and in transit
  • Password is not transmitted for recovery
  • Website lets you access encrypted backups 
  • Platforms: OS X (Java app), Windows, Linux, iOS, Android, Windows Phone
Cons: 
  • The archive key reset via reminder question is not a secure method
  • CrashPlan for Home requires a Java app, with security, reliability, usability issues
Code42’s CrashPlan offers three distinct options for setting up password and key control:
  • Standard: At the basic level, Code42 maintains on its servers an encryption key generated by its backup app. Your password manages access to the account as well as tasks like adding computers, using mobile clients, and restoring files.
  • Archive key password: The CrashPlan client generates a key, but you set a separate passphrase to encrypt the key, which is then stored in escrow at CrashPlan’s servers. You can upgrade from Standard to Archive without dumping existing backups. The archive key can be changed. There’s even an option to add an archive key reset with a reminder question. This reduces security enormously, however, because it effectively means your easier-to-remember answer is now the weakest link in accessing backups. I recommend against using it.
  • Custom key: You generate a lengthy key in one of several methods that’s never stored in any fashion at the Code42 servers. This custom key option is unique among services surveyed—all others rely on either a key generated by the app, which a user may be able to escrow at a server, or use an algorithm to convert a passphrase into the encryption key. If you switch from standard or archive key, your previous data is dumped, and you can’t downgrade encryption of newly archived files.
      
  • CrashPlan can decrypt files entirely via its native app. The archive key or custom key need only be entered when restoring files via the web interface, or viewing files via the web or the mobile apps.
    CrashPlan for Home still requires the use of a non-native Java app, something that’s been a security, reliability, and usability sticking point for its customers for years. Even its business services have moved to native apps. Java has many known security issues, but CrashPlan relies on it for a self-contained app, rather than any web-based interaction.

    iDrive and MozyHome

      Encryption rating: Fair 
    Pros:
    • Data is encrypted before and in transit
    • Password is not transmitted for recovery
    • Website lets you access encrypted backups Platforms: OS X, Windows, Linux (iDrive only), iOS, Android
    Con: 
    • Passphrase conversion carries some risk
    These two separate services work in nearly an identical way. Both let a user create a passphrase—iDrive inaccurately calls it  a “private encryption key”—which is transformed through a cryptographic algorithm into a 256-bit encryption key.
    When you use this option, neither the passphrase nor the resulting key gets transmitted to the service. Both iDrive and MozyHome also admirably handle decryption in their respective clients without sending the passphrase or key to a remote server.

Even though the key is never sent (good), this passphrase conversion approach is weaker (bad) than a passphrase that locks a separate encryption key. That’s because an attacker only needs to obtain your unencrypted passphrase or break it through brute force to have access to your key. With that, if they can obtain your backup archives from the services or capture them in transit somehow, they can decrypt.
While that scenario sounds unlikely, there have been exploits in the past that allow crackers to break encrypted data transmission. When a passphrase locks a separate encryption key, an attacker might need to obtain your account name and password and the passphrase, and then would either have to break into the backup service’s systems or log in directly and use the backup service’s interface to retrieve files, leaving a trail. 


Recommanded : Encrypt Your PC, Phone, and Tablet Now. You’ll Regret It Later If You Don’t

SpiderOak ONE

Encryption rating: Very Good 
Pros:
  • Data is encrypted before and in transit
  • Password is not transmitted for recovery
  • Website lets you access encrypted backups 
  • Highly granular shared secure data areas
  • Platforms: OS X, Windows, Linux, iOS, Android
Cons: 
  • If you want to share files or use the website, you have to enter the password
SpiderOak ONE is a bit of a hybrid between the iDrive/MozyHome and Backblaze approaches, and its sole method is highly secure—there’s no account password-only default tier.
With SpiderOak, you create a password in the desktop client, and the software derives many, many encryption keys from that. The password is never stored or transmitted to SpiderOak, but the keys—generated uniquely for each data block of the backup, each folder, and each file revision—are wrapped in a layer of encryption and stored on the backup servers.


This is because SpiderOak offers highly granular shared secure data areas, which require storing encryption keys on its servers in such a way that permission can be granted to multiple accounts to access files and folders. The same key can effectively be available to different users without storing it in such a way that SpiderOak (or a third party) can gain access.
In normal backup and restore operations, your password is never sent or used by the SpiderOak servers. However, if you want to share files, use the website for access, or use mobile clients, you have to enter the password to unlock access. As with other services, the keys generated from the password are stored in memory only while being used, and then flushed.

Should I Keep My Laptop Battery Plugged In All The Time?


Will my battery harm itself if the laptop is plugged in all time? It is one of the most searched battery-related questions on the internet. Some of you might be surprised to know that there’s nothing like “overcharging” a battery. Instead, you should avoid overheating your laptop and discharging its battery fully.

hile we talk about new gadgets and software all the time, we often ignore the batteries that provide the juice to power them. Similarly, our laptop batteries are one of the most important parts that often get ignored in the high octane discussions involving RAM and GPUs. Still, some battery-related questions keep on popping up regularly —  Should I keep my laptop plugged in all the time? Should I drain my laptop battery completely before charging?
Well, the answer to this question isn’t that simple. Before solving this query, let me tell some facts about your laptop battery that’ll help you understand the answer.

Here are some battery basics!

Most laptop batteries are either lithium-ion or lithium-polymer. These batteries are designed to withstand numerous charge cycles. These batteries can not be overcharged, which means that as soon as they are 100% charged, they stop charging. These batteries stop receiving energy which is bypassed directly to your laptop’s power supply. So, keeping it plugged in won’t harm your battery and cause much difference to the overall battery life. But, there are some other critical factors that we’ll be discussing later.
Another concept that one must keep in mind is that there are some good practices that extend the life of your laptop battery. Your battery has a finite number of charge-discharge cycles, so, discharging your battery completely repeatedly is going to harm its life.

Overheating is your battery’s biggest enemy!

You’ll be surprised to know that overheating is the most critical factor when it comes to the prolonged life of a battery. We told you above that keeping your laptop plugged in won’t kill your battery. True. But, you also need to take care of the excessive heating caused by laptop hardware.
So, if your laptop’s CPU/HDD temperature is around 40ยบC, keeping the laptop plugged in is fine. But, if your laptop has got a removable battery and you wish to use your laptop intensively, you are advised to remove the battery from the socket.

Recommended: You May Not be Able to Install Linux on Certain Microsoft Windows “Signature” PCs

So, what should I do? What’s the final answer?

Nowadays not all laptops come with removable batteries. So, removing the battery from the socket to cool it down isn’t a viable option. Instead, there’s a simple method that can help you extend your battery’s life in a different manner. According to the tests performed by Battery University, a battery that is charged to 100 percent will have only 300-500 discharge cycles. One the other hand, if it’s charged to 70-80%, it’ll get 1000-2000 recharge cycles.
Based on what I’ve told you in this article, here are some notable points:
Avoid discharging your laptop completely after charging it. The best thing you can do is try to keep the battery level between 40 percent to 80 percent.
Make sure that your laptop doesn’t get too hot and your cooling fan is working properly.
Your laptop battery can’t “overcharge” and harm itself due to excessive charging. It’s smart enough to bypass the charging energy.
Did you find this article helpful? Don’t forget to drop your feedback in the comments section below.

How To Delete Your Facebook Account Permanently


Short Bytes: Sometimes you want to get out of the Facebook world. Most of the people know about deactivating their Facebook. But it is also possible to delete your Facebook account permanently. But do remember to download a copy of your Facebook data before deleting your account.

acebook is the biggest social network in the world with around 1.13 billion active users per day. An uncountable number of profiles are created every day. Many people post almost all of their life activities on Facebook and for some people, it’s only a medium to remain connected with their old friends and remember their birthdays.
Sometimes you want to get out of your Facebook life and enjoy the real world. You do this by deactivating your Facebook account. But you can also delete your Facebook account permanently if you want to leave Facebook for the rest of your life.

Backup your Facebook data

Before saying goodbye to your Facebook life, you should backup your data in case you need it at a later point in time.
  1. Go to Settings.
  2. While in the General tab. Click Download a copy of your Facebook data.
  3. Click Start My Archive.


  1. Enter your Facebook account password. Click Submit.
  2. Click Start My Archive in the Request My Download box.
Facebook will then gather all your data and send the copy to your registered email address.

How to deactivate your Facebook account?

It’s simple. You might be thinking why I am telling you such simple thing. If you know how to deactivate your Facebook account, it’s good. But some people might not be aware of this. Here are the steps to deactivate your Facebook account:
  1. Go to Settings.
  2. Click Security in the left pane.
  3. Click Deactivate your account.

How to delete your Facebook account permanently?

One thing that most users want to know is how to delete Facebook account permanently. For this, follow the steps:
  1. Log into your Facebook account.
  2. Visit this link, https://www.facebook.com/help/delete_account
  3. Click Delete My Account.

  1. I can’t go further as I don’t want to delete my Facebook account. So, go ahead yourself.

Important things to consider before deleting your Facebook account

Make sure you’ve downloaded a copy of your Facebook data before deactivating or permanently deleting it. You might be aware of the fact that you can gain access to your Facebook account after you’ve deactivated it. But be careful, you won’t get the chance to change your mind after you’ve deleted your Facebook account permanently. So, take your decision wisely.
It will take 90 days for Facebook to delete all your photos, videos, posts, likes, comments, messages, and everything else. Other Facebook users won’t be able to visit your profile during the deletion process. However, the text messages, images you’ve sent to your friends via chat will reside at their end because they’re a part of their account also. You can ask them to delete your messages.

Protect your Mobiles, Laptops Cameras from Hackers And Government.


As we are surrounded by technology, It’s important for users to continue taking care of their privacy, technology has made our life simpler, there are always some people which will try to exploit into your personal life by hacking into your life, through technologies, by spying on you.


Snowden Revealed Government Surveillance on Everyone in 2013. They are not just targeting their own citizens but also foreign dignitaries and diplomats. It’s not that hard for hackers to target anyone and record through your webcams.
HackRead Reported!

Here’s How to Protect yourself!

Covering the phone camera.
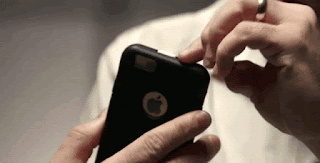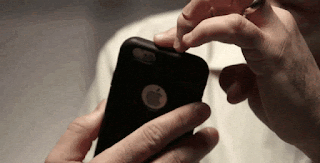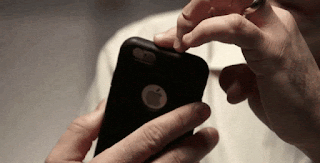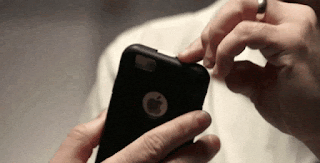
The EyePatch Case works through the use of a switch. When you flick the switch cameras on both ends of the phone are covered completely. Simple indeed. It’s a useful physical solution to a digital problem.


 Hiding laptop camera


In case you want to buy a special laptop cam cover to give a neat look while hiding the cam at the same time, you can also buy one online or from a cell phone accessory store.


On a serious note if you can’t find a sticker just put a band aid.


EndNote
After all, this is said and done; we still need to take into account Snowden’s revelations. The government was unknowingly spying people. And how can we stop the snooping? A sticker!! Yes, low-tech solutions to high-tech problems. Another way to stop the intrusion of microphones is by using dummy plug into the microphone jack which would prevent the hacker from picking up the sound with their internal mic

11 Tips for Safe Online Shopping


Let's face it, there's every reason in the world to shop online. The bargains are there. The selection is mind-boggling. The shopping is secure. Shipping is fast. Even returns are pretty easy, with the right e-tailers. Shopping has never been easier or more convenient for consumers.
But what about the bad guys who lay in wait? IID's Third Quarter eCrime Report for 2011 indicates that use of phishing attacks (where thieves attempt to swindle you out of your sign-in credentials and even credit card info by pretending to be a real website, or even an online bank) is down, as much as eight percent since the second quarter and 11 percent since the third quarter of last year. That's great news—except the same report says sites with malware (malicious code aimed at compromising your privacy) has increased by 89 percent since the second quarter.

Stay calm. While somewhat alarming, these stats should not keep you from shopping online. You simply need some common sense and practical advice. Follow these basic guidelines and you can shop online with confidence. Here are 11 tips for staying safe online, so you can start checking off items on that holiday shopping list.
1. Use Familiar Websites
 
Start at a trusted site rather than shopping with a search engine. Search results can be rigged to lead you astray, especially when you drift past the first few pages of links. If you know the site, chances are it's less likely to be a rip off. We all know Amazon.com and that it carries everything under the sun; likewise, just about every major retail outlet has an online store, from Target to Best Buy to Home Depot. Beware of misspellings or sites using a different top-level domain (.net instead of .com, for example)—those are the oldest tricks in the book. Yes, the sales on these sites might look enticing, but that's how they trick you into giving up your info.
2. Look for the Lock
 
Never ever, ever buy anything online using your credit card from a site that doesn't have SSL (secure sockets layer) encryption installed—at the very least. You'll know if the site has SSL because the URL for the site will start with HTTPS:// (instead of just HTTP://). An icon of a locked padlock will appear, typically in the status bar at the bottom of your web browser, or right next to the URL in the address bar. It depends on your browser.

Never, ever give anyone your credit card over email. Ever.
3. Don't Tell All
 
No online shopping store needs your social security number or your birthday to do business. However, if crooks get them, combined with your credit card number for purchases, they can do a lot of damage. The more they know, the easier it is to steal your identity. When possible, default to giving up the least amount of information.
4. Check Statements
 
Don't wait for your bill to come at the end of the month. Go online regularly during the holiday season and look at electronic statements for your credit card, debit card, and checking accounts. Make sure you don't see any fraudulent charges, even originating from sites like PayPal. (After all, there's more than one way to get to your money.)
If you do see something wrong, pick up the phone to address the matter quickly. In the case of credit cards, pay the bill only once you know all your charges are accurate. You have 30 days to notify the bank or card issuer of problems, however; after that, you might be liable for the charges anyway.
5. Inoculate Your PC
 
Swindlers don't just sit around waiting for you to give them data; sometimes they give you a little something extra to help things along. You need to protect against malware with regular updates to your anti-virus program. PCMag recommends Webroot SecureAnywhere Antivirus (4.5 stars, Editors' Choice, $39.95 direct), which has extras to help fight ID theft, or at the very least the free Ad-Aware Free Internet Security 9.0 (4.5 stars, Editors' Choice)

Six ways to backup your data


Today is World Backup Day, and it goes without saying that backing up data is a thoroughly sensible thing to routinely get into the habit of doing.
Not only does it make sense in case your laptop is stolen, or your hard disk fails, but it also means that you have more options for recovery should your computer become infected with ransomware, a particularly nasty strain of malware. Ransonware encrypts your files and threatens to delete them if you don’t pay a ransom within a certain time period. ESET doesn’t recommend giving in to ransomware demands for many reasons both ethical and practical (not least because you mark yourself as a possible target for future attacks), but if your files are all safely backed up, you won’t even feel tempted to negotiate with them in the first place.
There are plenty of options available for people looking to backup up their data, all with their own pros and cons. In this article we have listed some of your options, but remember: it’s best to have more than one backup to be safe. This is particularly true in the case of ransomware. For example, if you back up your computer to an external hard drive, but leave that drive connected when you are not doing backup, some ransomware will try to encrypt those backup filed as well: always disconnect backup drives when the backup has finished.
1. USB stick


Small, cheap and convenient, USB sticks are everywhere, and their portability means that they’re easy to store safely, but also pretty easy to lose. There are questions about the number of read/write cycles they can take, so should be considered alongside other backup methods.
Pros:
+ Extremely portable
+ Very cheap
+ Can easily transfer data to other sources
Cons:
– Portability means they’re small and easy to lose
– Questions over read/write cycle longievity
2. External hard drive


External hard drives are just what they sound like – hard drives that live outside your computer, meaning they can be plugged in to other sources. If using them for backup, it’s best not to use them as an ‘extra every day hard drive’.
Pros:
+ Relatively cheap
+ Plenty of storage space for larger files
Cons:
– Potentially open to problems which lost files in the first place (a power surge or malware)
3. Time Machine


For the Mac users out there, Time Machine is an option that backs up to external hard drives automatically. Apple sells  its own brand of dedicated wireless Time Capsules, but you can use any hard disk for it. Using this method, you’ll automatically keep backups hourly for the last 24 hours, daily for the last month and then weekly backups until the machine is full.

Pros:
+ Automated, meaning you shouldn’t forget to stay up to date
+ Frequency of backups means you should never be too out of date
+ Backs up whole drive, not just the key files
Cons:
– Dedicated wireless machine is expensive
– Mac only
4. Network Attached Storage


Businesses tend to backup their files to network attached storage, but with more and more homes having multiple computers, the idea has a certain appeal, especially for those looking to save files from more than one source. With prices coming down, a dedicated wireless storage solution is a convenient option which requires less thought.
Pros:
+ Automatic backups mean you don’t risk forgetting
+ Wireless solutions also work with phones and tablets
Cons:
– Can be expensive
– Can be awkward to set up and maintain
5. Cloud Storage


While network attached storage is essentially your own Cloud Server, there are plenty of third party cloud storage options around: free, paid, or free with paid extras. iCloud, Dropbox, Google Drive and OneDrive are big names, but others are available.
Pros:
+ Can be done automatically
+ A certain amount of space is usually free
+ Device agnostic
Cons:
– Requires an internet connection to work
– You can’t account for their security breaches
– Companies aren’t obliged to keep these services around forever
6. Printing


At a first glance, this might sound a facetious inclusion. But while considerably less technically advanced, printing offers you a hard copy of your most important documents that will survive power outages, and are easy to store and access even if your computer is out of action for a few days. Of course it’s hard to keep documents up to date this way, and it won’t work for video or audio files, but for that novel you’d be devastated to lose, it’s certainly worth considering.
Pros:
+ A backup that won’t be affected by hardware outages or tech headaches
+ Impossible for hackers to access
Cons:
– Impossible for certain file types
– Awkward to manage
– Less practical for longer documents
– Not great for the environment
However you choose to backup your data (and it’s smart to consider using more than one solution, at least for your life-or-death files), make sure that you do it. Often people don’t think about what were to happen if their valuable files were to be lost, until it’s too late. Don’t make that mistake, and use World Backup Day to make sure your files are all safe and accounted for.

5 security questions to ask before clicking on a link


URLs used to be a nice and simple way to link to an online destination without a long and fiddly URL, but in today’s world of advancing cybercrime they can lead to password and data theft, even drive-by-download malware attacks. So ask yourself these five questions before clicking on that shortened link.

Do you trust the person sending/posting the link?

‘Trust’ should be the same online as it is in the real world, but sadly this is rarely the case. For example, people will always check the keyhole before opening their front door, and teach their children about the dangers of walking off with strangers, but these same people might also open an email, or click on a link, from someone they’ve never met.
The good news is that, despite phishing remaining a popular tool for cybercriminals, people are improving at distinguishing the good emails (and links) from bad, something that has also been helped by advancing spam filters.
Nonetheless, you still need to be alert, so the first question to ask yourself is ‘do I trust the person sending or sharing this link?’ If the link has been sent by a friend or family member, and on a trusted social media platform or email client, there’s a good chance it’s OK. If, for whatever reason, you’re unsure, maybe you could call them to verify that they did indeed send that information.
However, if you don’t recognize the name, the email account or the content, it is best avoided. You should be particularly wary of emails that look to catch you out by mentioning your name in the subject matter, or which claim to be from your bank or PayPal account.

Do you trust the platform?


Like most of the questions on this list, ‘do you trust the platform?’ revolves around common sense. For instance, there’s probably no need to worry if this link has been shared on your businesses’ Intranet or private WhatsApp group. But if something’s in your email spam, or on an anonymous Twitter account, that should be treated with caution.
Pay special attention to Twitter and Facebook as both social media websites have been hit by copious amounts of spam before, with some links even directing users to malware-infected websites. If you’re unsure on the link, and don’t know about the platform, you should search elsewhere.
Additionally, high profile accounts have been hacked, so if the surrounding text seems out of character for the sharer, think twice.

Do you trust the destination?

Look at the link that has been shared. Does it go to a website you recognize, or even like?
If you don’t trust, or don’t know, the destination you should not click the link. Instead, do your own web search and visit the website via that route.

Does this link coincide with a major world event?


Cybercriminals are very opportunistic, and they’ll seize any opportunity to get someone to click that link that takes them to a bad website. This is especially true around major events, like natural disasters, Olympics and World Cups – the numbers of spam emails and tweets simply skyrocket at this time; just take a look at the emails sent shortly after the MH17 disaster.
So if you see a link, for example on the Nepal earthquake, have a good hard think about this, in relation to the three previous questions on the source of the link, where it has been shared and where the link is taking you to.

Is it a shortened link?

The rise of social media like Twitter, Facebook and Instagram has seen the rise too of shortened links for convenience. Most of these are well intentioned but danger can still lurk here.
For example, a cybercriminal can shorten their nefarious link using Bitly, goo.gl or any other provider, in the hope that the user blindly trusts that link as from a trusted source. Also, if they combined this link with an authentic tweet or email, the user could well be encouraged into thinking that this was a legitimate message from a legitimate user.
So with shortened links, the advice is clear; ask yourself the above four questions and if you’re unsure still, use the likes of LongURL and CheckShortURL, to restore the shortened link to its original length.

How to delete your smartphone data securely before selling your device


Some people change their smartphone or tablet almost as casually as they change their clothes. They buy and later sell mobile devices without the slightest concern about the information that, one device after another, they keep putting in the hands of total strangers. This article is aimed at all those people, and in it you will be able to learn what measures you can take to protect your privacy.

When you delete a file, is the data really deleted?

Unfortunately, no. With most IT equipment, deleting a file means telling the system that the next time it needs to write data, it can overwrite the space used by the file in question.
However, until the new write operation takes place, the information remains physically stored in the form of bits on the corresponding storage drive and can be recovered. This kind of deletion is known as logical deletion and is the procedure that almost all operating systems use.
In contrast, there is another kind of deletion called physical deletion which modifies the data bit by bit, by creating junk content on the storage medium. This procedure ensures that the data cannot be recovered, but it takes much longer and therefore usually is considered undesirable for tasks where the user experience is central.

What happens if you restore to factory settings?

That depends on the platform. Research carried out in early 2015 showed that on Apple and BlackBerry devices, when you perform a factory reset, the deletion of data is physical, thus preventing the information from being recovered later. However, not all Android devices were as lucky and it was possible to recover a lot of the data that had been stored on them.
According to the researchers, the reason for this could be that Apple and BlackBerry have better control over their hardware and so can wipe the data on the device more effectively. Given that operating systems like iOS use encryption built into the hardware by default, factory reset only actually needs to delete the encryption keys physically.
In contrast, encryption is not included by default on Android and, according to the researchers’ findings, information can be recovered even after running several factory resets.

What are the dangers of logical deletion?

Cell phones are very personal devices. Using them involves the use of totally private data, like credit card details, purchase records, contact details of friends and family, videos, photos (possibly including nude images of the user), schedules, geolocation, files and their associated metadata, web browser history, Wi-Fi connection history, logins and passwords for email and other cloud-based services, text messages, chats logs on social media, and a great deal of other information.
All this smartphone data could potentially provide material enabling a cybercriminal to orchestrate a social engineering attack against the handset’s owner. Unfortunately, as some people have experienced first-hand, if this information falls into the wrong hands it can even lead to extortion and fraud in which the criminal blackmails the user by threatening to distribute the data.
Another great worry is that strangers might gain access to user accounts for apps installed on the device, like online shopping, banking, and social network apps. For this reason, taking preventive measures will enable us to feel more at ease and be better protected against such risks.

How can another person recover our personal information?

There are numerous tools designed to recover data stored physically on a mobile device. These utilities are known as forensic analysis tools and normally are used to break down the sequence of actions that led to an IT incident or to find evidence that could lead to a verdict in a court case.
However, some of these tools are free and can be accessed by people with malicious intentions to gain information they should not have access to.

So, how can you protect yourself?

As we already mentioned, for iOS users, a factory reset is sufficient. But what should Android users do? The simplest option for making it difficult to recover data is to encrypt the device before restoring the factory settings. That way, although someone could make a physical copy of the device, the bits of data stored on it will not make any sense to them.
Given that the decryption keys are, in turn, protected by the password set by the user, and even in the event of an unsuccessful reset, the attacker would have to carry out a brute force attack against the keys in order to gain access to them. And let’s not forget that the more complex the password, the more difficult it will be to crack. This means that although encryption is not an infallible form of protection, it’s enough to discourage most cybercriminals.
You can encrypt your Android system by going to Settings > Security > Encrypt device, and the reset options are located in Settings > Backup & reset > Factory data reset. Another way to format the memory is by accessing the device’s recovery mode, however, the results of this method are the same.


It is also possible to find apps on Google Play Store that promise to overwrite the parts of the memory that have been marked as free by the operating system, but that might still contain the original data. The user will need to carry out a factory reset both before and after running the app. In addition, they will need to avoid using Google Play Store to install the app on the cell phone, so as to avoid entering their Google account data into the phone again.
Finally, don’t forget to remove the SIM card and also the micro SD card. Now that you know how to wipe your data, be sure to protect your privacy before getting rid of a device.